Attack signatures
It reads every request for attacks.
In the spirit of the OWASP Core Rule Set, the edge looks for seven families of attacks in the path, the query, cookies, headers and the first 16 KB of form, JSON, text and multipart bodies.
- Log, ask for a browser check, or block with 403
- Three sensitivities, from almost never wrong to broad
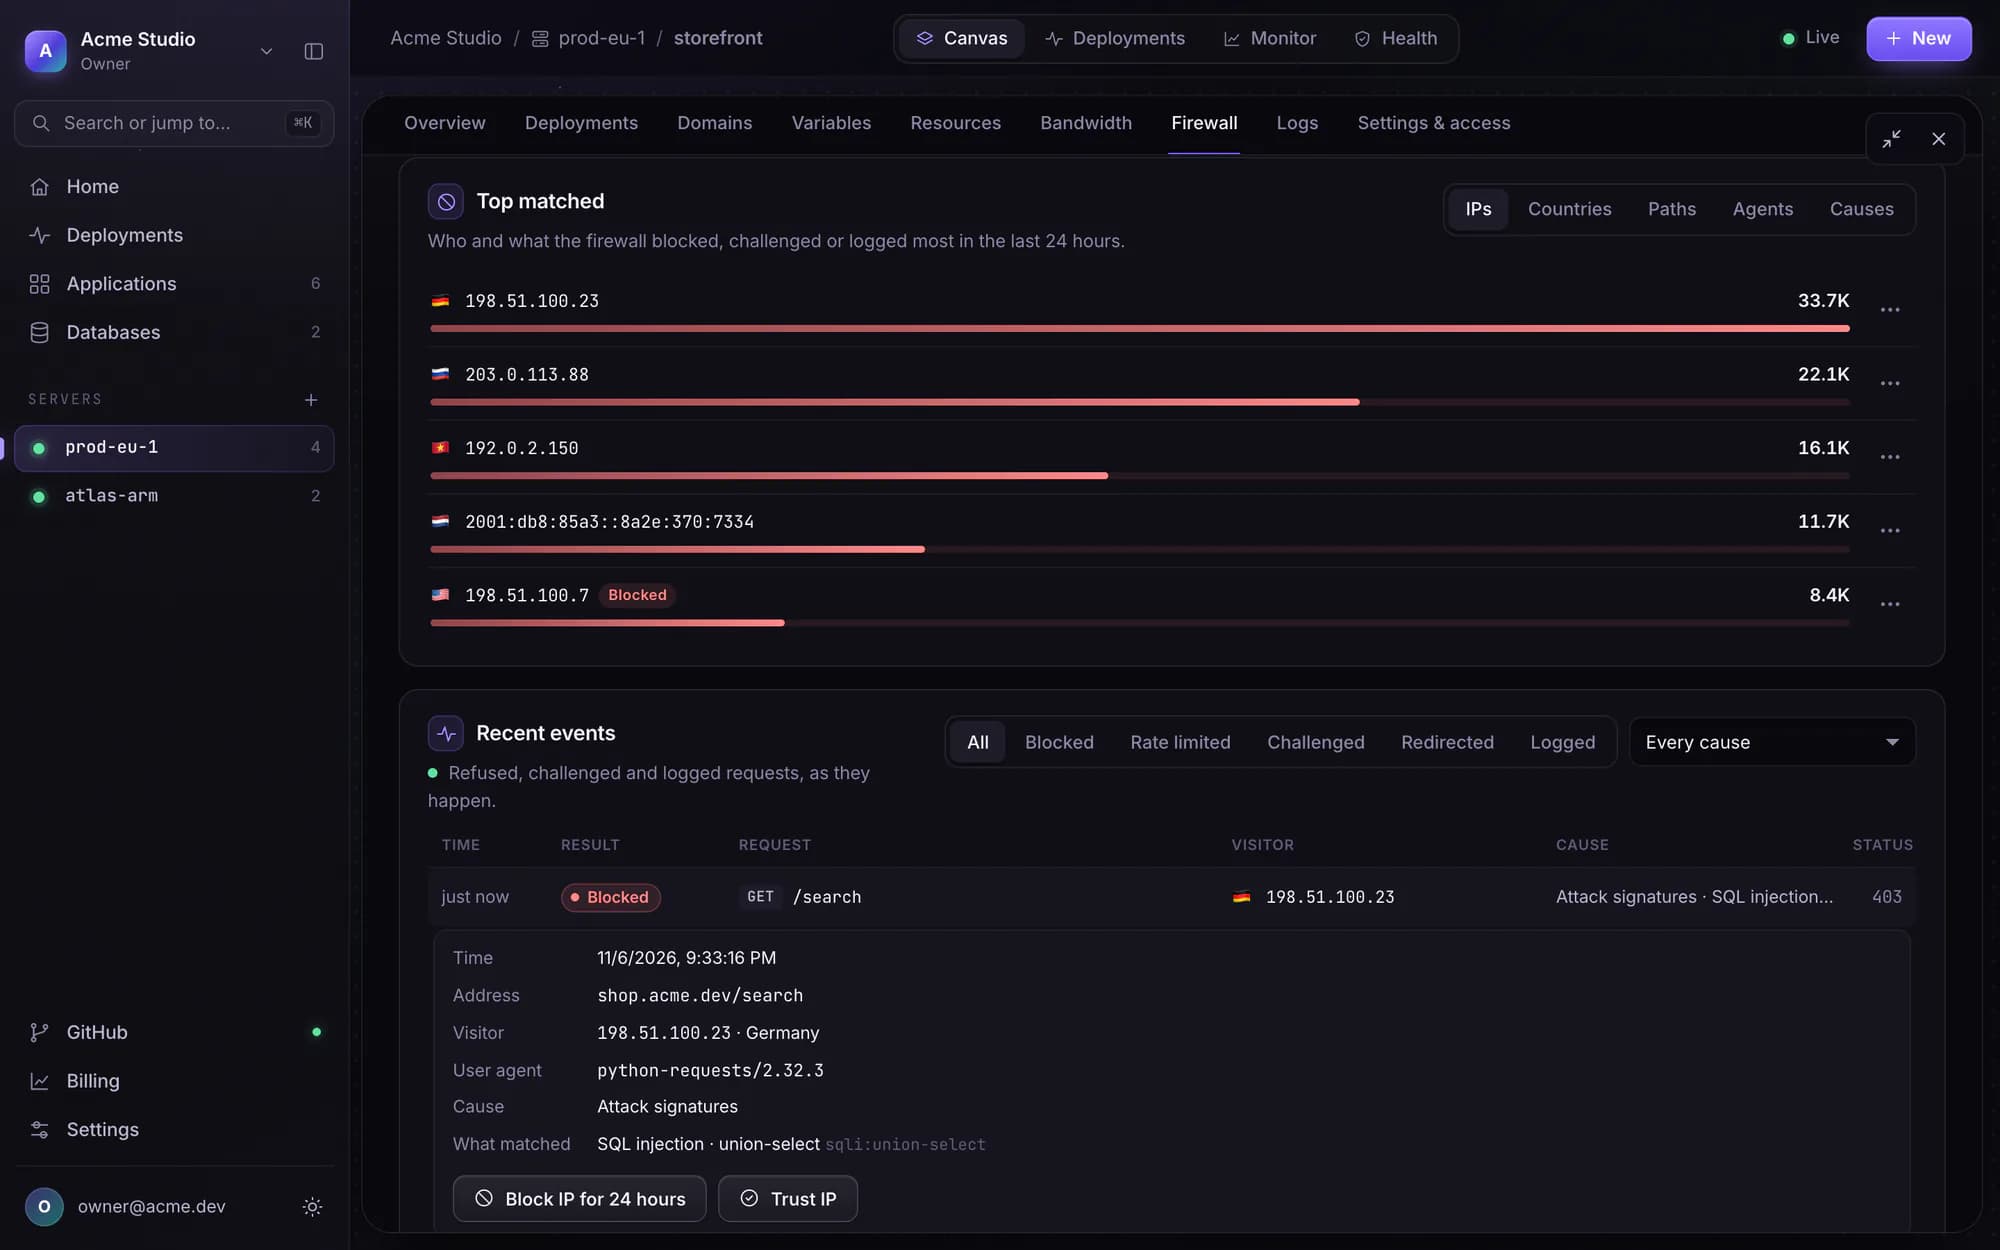
- Every event names the signature, like sqli:union-select
- Padding can't hide an attack: oversized values count as a detection
- Password fields are never inspected, and the check costs microseconds
Inspected at the edgeExample
GET /search?q=1' union select email, password from users--
User-Agent: Mozilla/5.0
Cookie: cart=3
Blocked · 403SQL injection · sqli:union-select
- SQL injection
- Cross-site scripting
- Path traversal
- Command and template injection
- Log4Shell, Spring and OGNL
- PHP injection
- SSRF
ModeOffLog onlyBrowser checkBlock
SensitivityLowMediumHigh